
NIST CSF 2.0 Assessment
See where your security stands today, and where to take it next. IT Hawaii's NIST CSF 2.0 assessment scores your business across all six CSF functions and gives you a prioritized plan, with the quick wins first, anywhere in Hawaii.

Your starting point for a stronger security program
NIST CSF 2.0 is the cybersecurity framework from the U.S. National Institute of Standards and Technology. It organizes security into six functions: Govern, Identify, Protect, Detect, Respond and Recover. Our assessment is the first step when we build your cybersecurity program, and you can also buy it on its own.
How the assessment works
Our cybersecurity team talks with your owners, managers and key staff about how your business runs. We review your systems, settings, accounts, backups and security tools, along with your policies, procedures and vendor contracts. Then we score your business across all six CSF functions.
Your next move, your choice
You can turn the action plan into a cybersecurity program that IT Hawaii builds and manages with you, work through it with your own IT, or hire us for specific fixes. You can also put the results toward compliance work for HIPAA, PCI DSS, SEC Regulation S-P or CMMC, and toward security questionnaires.

What you get
Clear answers about your security, ready for your owners and your IT team.
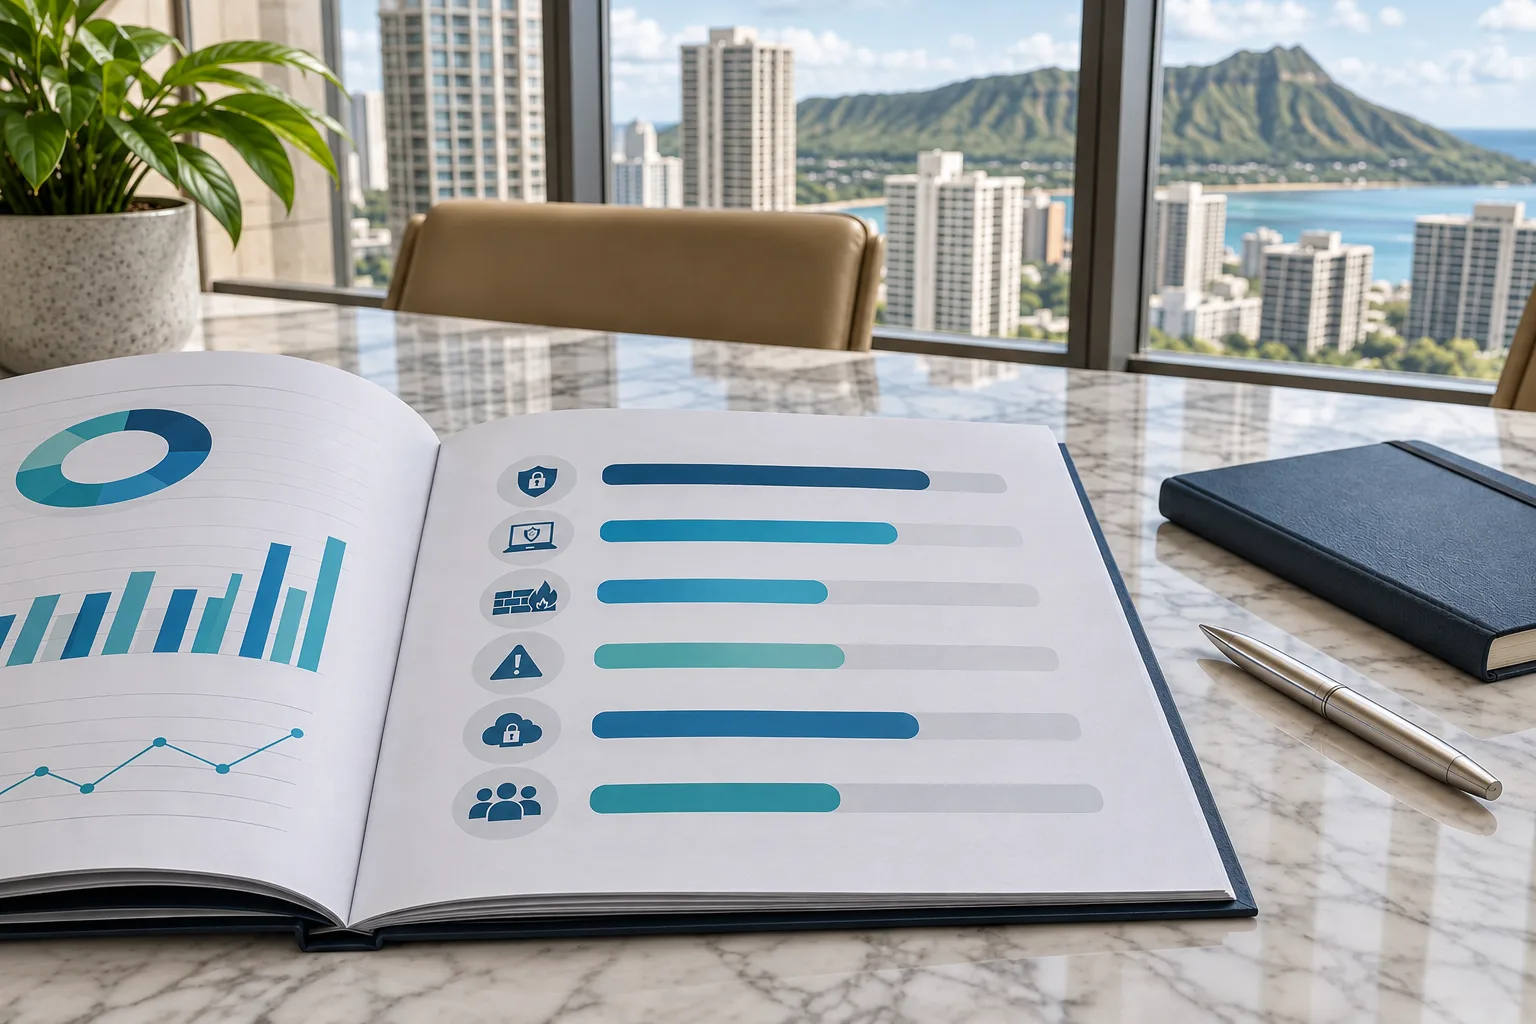
Written report
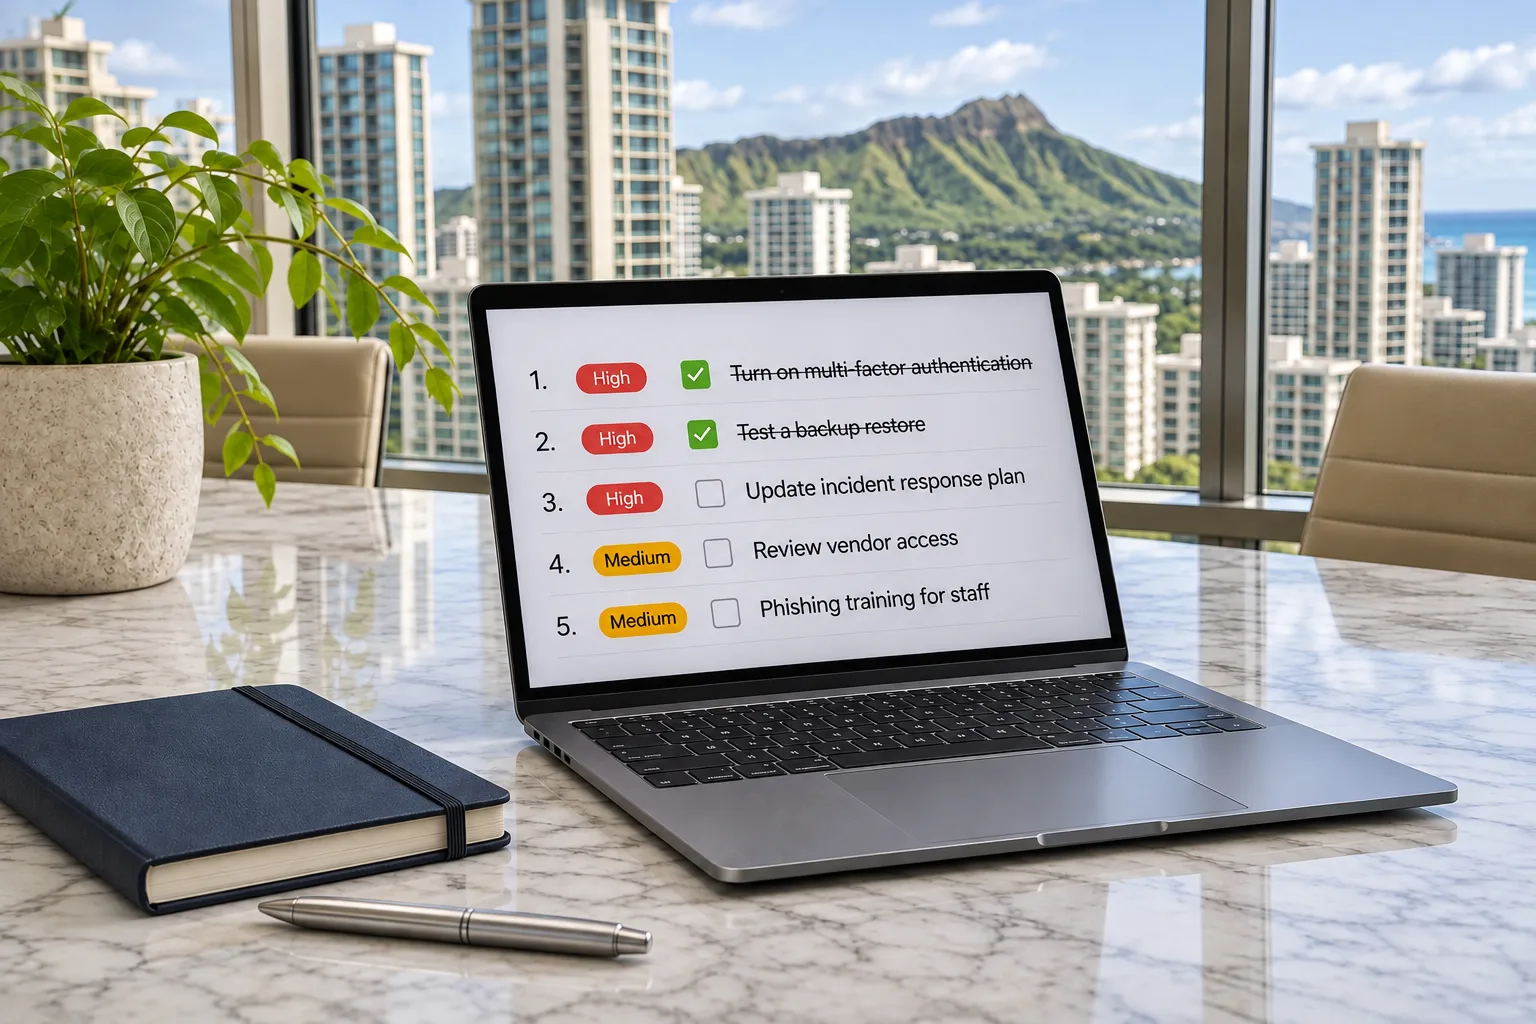
Prioritized action plan
Current and target profiles
Leadership walkthrough
Ready to see where you stand?
Tell us about your business and your IT setup. The assessment is for Hawaii businesses with 10 or more employees and works alongside your current IT provider or in-house team. A real person will reach out within one business day.
Frequently asked questions
A NIST CSF 2.0 assessment measures a business's cybersecurity against the NIST Cybersecurity Framework 2.0. IT Hawaii's assessment scores your business across the framework's six functions (Govern, Identify, Protect, Detect, Respond and Recover) and gives you a written report and a prioritized action plan.
A written report of findings and scores, a prioritized action plan with the quick wins first, current and target profiles, and a meeting that walks your owners or leadership through the results.
Yes. You can use the results toward HIPAA, PCI DSS, SEC Regulation S-P or CMMC work, and toward security questionnaires from insurers, clients and vendors.
Interviews with your owners, managers and key staff; a technical review of your systems, settings, accounts, backups and security tools; a review of your policies, procedures and vendor contracts; and scores across all six CSF functions.
Yes. You can buy the NIST CSF 2.0 assessment on its own. It's also the first step when IT Hawaii builds a cybersecurity program.
Hawaii businesses with 10 or more employees, anywhere in the state. It works alongside your current IT provider or in-house team.